jev-sec-audit Flags Risky npm Packages
jev-sec-audit uses Jev, a System 1 model built for fast decisions, to flag risky npm installs. It runs as one step in GitHub Actions and is open source.
 Dhanush N@Dhanush_Nehru
npm install is the scariest command in your terminal.
One typo → lookalike package → malicious postinstall → secrets gone.
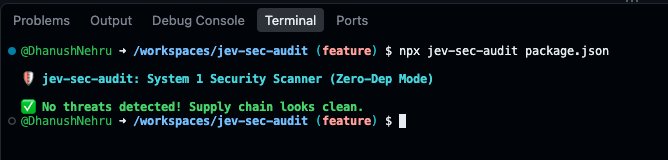
jev-sec-audit flags it in milliseconds using Jev, a System 1 model built for fast decisions, not chat.
One step in GitHub Actions. Open source.
https://t.co/PhC7TLRwCt
The post warns that a typo can lead to a lookalike package. A malicious postinstall can put secrets at risk.
Also filed under Tools & apps
- Google Icons Search Tool
Roman Khrupa built a tool that searches Google Icons using JEV (Laya-MLX).
- Query workload classifier for Postgres
A desktop app that uses Jev to classify your entire query workload and tell you which queries to EXPLAIN ANALYZE first.
- AI Slop Finder for X
Utkarsh Singh built an AI-slop finder for X using Jev. A content script extracts tweet text, sends it through a backend API to Jev, and displays the resulting AI-slop score as a badge on the tweet.
- Enforce CLAUDE.md With Jev
The build uses Jev to check Claude’s final replies and edits against rules in CLAUDE.md. It sends violations back to Claude to fix in the same turn.